Webinar: IGA Built On and For ServiceNow — The Best of Both Worlds
Watch Past Webinars covering real customer use cases in Identity, Access, and JML Automation

Entra–Okta Integration: How to Stop Access Drift

Nowadays, employees move fast, but identity systems don’t keep up. That gap between how quickly people join, move and leave, and how slowly digital access catches up, is where delays, security gaps and compliance issues quietly build. Most organisations don’t realize how much drift exists until it creates a real incident.

A lot of companies today run Entra ID and Okta side by side. Entra ID powers the Microsoft ecosystem, and Okta handles third-party and cloud apps. On paper, it sounds like a balanced setup. In reality, these systems often operate in silos. According to a recent global study by CyberArk, 93% of organisations experienced two or more identity-related security breaches in the last year, and disconnected identity sources are a major contributor to those incidents. When HR updates don’t sync instantly across both platforms, permissions fall out of date, old access lingers, and teams start relying on manual fixes that can’t scale.

When access isn’t updated on time, IT teams scramble to manage new hires, exits and role changes across two separate identity stores. This is where delays turn into security risks, and minor gaps turn into compliance problems. And this isn’t happening in a handful of companies; it’s happening everywhere, across tech, retail, finance, healthcare and even education.

Where the Breakdown Really Happens

Most of the trouble starts with the HR system. When an employee joins, leaves, or changes roles, HR updates the record. But Entra ID and Okta read those changes differently. Without a reliable automation layer, you end up with:

New hires are waiting for access
Contractors receiving more access than they need
Employees carrying old permissions into new roles
Ex-employees keeping access to SaaS apps long after exit

Each small delay compounds into a bigger identity drift. IT teams try to bridge the gap manually with tickets or scripts, but none of these scales. Every manual step increases the odds of mistakes.

Why the Entra–Okta Identity Gap Matters

Identity mismanagement isn’t a small leak; it’s a widespread issue with very real consequences.

A significant share of breaches in recent years is tied to weak or outdated access controls.
Many companies admit that former employees still have access to critical systems weeks after leaving, simply because their identity sources don’t sync.
Security teams report that mismatched identities across platforms Entra, Okta, HRIS such as ADP or Workday, and other tools, are one of the top drivers of manual workload and audit findings.
Delayed provisioning is one of the biggest bottlenecks in onboarding, hurting productivity right from day one.

When two major identity systems operate in silos, oversight becomes almost impossible. This isn’t a corner-case problem anymore. Any place that uses both Entra ID and Okta is almost guaranteed to run into this friction.

Why Solutions Like Hire2Retire Solve the Identity Automation Problem

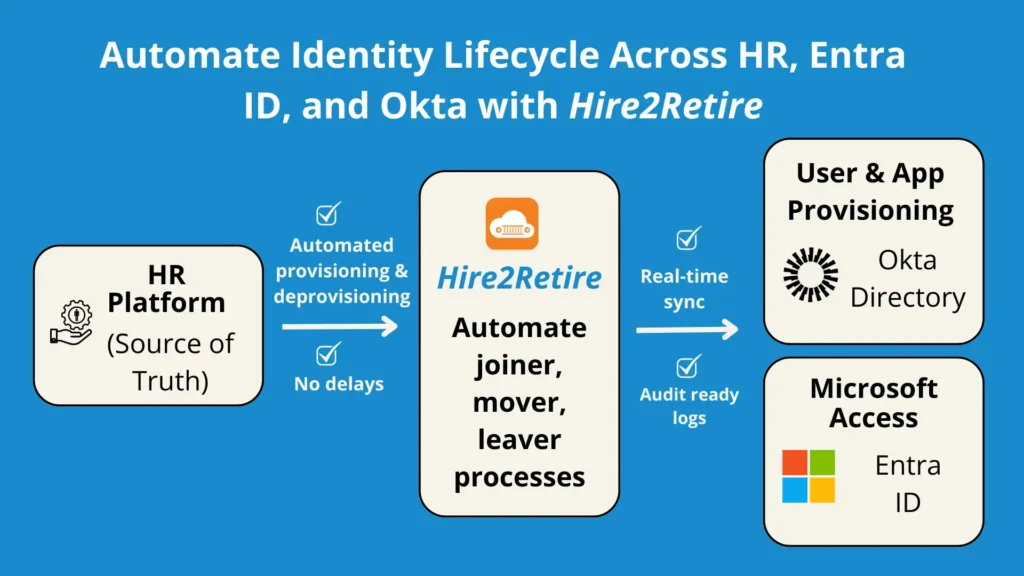
Hire2Retire by RoboMQ is an Identity, Governance & Administration solution that provides zero-touch automation of workforce identity, access and privileges from HR as the source of truth to identity systems for Joiner, Mover and Leaver (JML).

Hire2Retire sits between your HR system, Entra ID, and Okta. It translates every HR change into real-time identity action across both platforms. No tickets. No delays. No mismatched profiles.

Here’s what it brings to the table:

Real-time provisioning and deprovisioning in both Entra and Okta
Accurate role and group assignment based on HR data
Fully automated access removal at the moment of exit
Audit-ready logs and complete process transparency
Less IT workload and fewer security gaps

Instead of HR pushing changes to one system and IT manually fixing the other, everything flows automatically and consistently.

Case Study: How Everise Fixed Identity Drift

Everise, a customer-experience company with over 10,000 employees across multiple locations, found itself scaling fast and running into identity-management strain. As the organisation expanded, its HR system (Workday) held accurate employee data, but it wasn’t integrated with its Active Directory environment. The result: manual account creation, delayed de-provisioning and a growing risk of orphaned accounts.

IT teams were spending hundreds of hours creating user profiles, assigning groups and cleaning up duplicate or inconsistent identities. And because the systems didn’t sync automatically, employee exits didn’t always lead to immediate access removal. That gap is exactly the kind of risk that appears when identity sources don’t talk to each other.

After deploying an automated lifecycle integration solution (Hire2Retire), Everise made onboarding and offboarding almost instant. They enforced consistent naming conventions, eliminated duplicates and ensured access was assigned based on Workday-driven attributes such as department, location and role. It’s a clear example of how lifecycle automation boosts operational efficiency while tightening security by eliminating access drift.

Final Thoughts

If your organisation uses both Entra ID and Okta, identity drift isn’t a hypothetical problem. It’s already happening in the background. The good news is that it’s fixable. Automation bridges the gap that manual processes can’t.

Hire2Retire gives you a consistent, secure, and scalable way to manage identities across both platforms without relying on tickets, reminders, or human intervention. It keeps your access clean, your audits smooth, and your employees productive.

If you’d like to see how automated provisioning, real-time updates and clean offboarding actually work, schedule a free Hire2Retire demo.

Frequently Asked Questions (FAQs) 

Access drift occurs when a user’s permissions in one system (like Okta) become inconsistent or misaligned with their true, current access rights in the other system (Entra ID/Azure AD).

The Entra-Okta identity integration gap allows users to retain excessive or outdated access in one platform even after it’s been revoked in the other, creating a major vulnerability for attackers or compliance issues.

The lack of synchronized identities creates support tickets and delays because IT staff must manually fix and reconcile user permissions across different platforms.

The goal is to establish unified access control and ensure the Principle of Least Privilege is consistently applied across all applications governed by either identity provider.

It provides a Superior “First Day at Work” Experience by automatically provisioning all accounts, licenses, and role-based access in minutes, eliminating the common delays that hinder new employee productivity.

Picture of <strong>Sujata Swarnim

Sujata Swarnim

Sujata Swarnim is a Marketing Enthuasiast with a majors in Marketing , working at RoboMQ. She thrives on connecting the dots, between people, ideas & opportunities - turning creative insights into meaningful impact & power brand stories.

Picture of <strong>Sujata Swarnim

Sujata Swarnim

Sujata Swarnim is a Marketing Enthuasiast with a majors in Marketing , working at RoboMQ. She thrives on connecting the dots, between people, ideas & opportunities - turning creative insights into meaningful impact & power brand stories.

Entra–Okta Integration: How to Stop Access Drift

Use Cases

Entra–Okta Integration: How to Stop Access Drift


Posted onNovember 14, 2025
How To Entra–Okta Integration: How to Stop Access Drift Use Cases Sujata Swarnim November 14, 2025 Nowadays, employees move fast, but identity systems don’t keep up. That gap between how quickly people join, move and leave, and how slowly digital access catches up, is...
Strengthen Security with Identity Lifecycle Management

Use Cases

Strengthen Security with Identity Lifecycle Management


Posted onNovember 11, 2025
How To Strengthen Security with Identity Lifecycle Management Use Cases Sujata Swarnim November 11, 2025 Nearly 43% of companies fail to fully revoke access for ex-employees, allowing them to retain entry to sensitive systems like code repositories. Paul, a senior...
Workforce Management: The Smarter Way Forward

Use Cases

Workforce Management: The Smarter Way Forward


Posted onNovember 7, 2025
How To Workforce Management: The Smarter Way Forward Use Cases Sujata Swarnim November 7, 2025 Over 70% of enterprises admit their employees retain system access even after leaving the organization. Every employee journey leaves a digital footprint – logins,...
User Access Management: Securing Enterprise access

Use Cases

User Access Management: Securing Enterprise access


Posted onNovember 6, 2025
How To User Access Management: Securing Enterprise access Use Cases Sujata Swarnim November 6, 2025 A new hire is onboarded in your organization, but your IT team doesn’t get the update for hours, sometimes days. A contract employee gets temporary access to multiple...
Paycom to AD Integration: Reduce Manual Effort

Use Cases

Paycom to AD Integration: Reduce Manual Effort


Posted onNovember 4, 2025
How To Paycom to AD Integration: Reduce Manual Effort Sujata Swarnim November 4, 2025 IT teams at many enterprises spend up to 30-40% of their productive hours on manual user account management tasks, like creating new accounts, updating permissions, or...